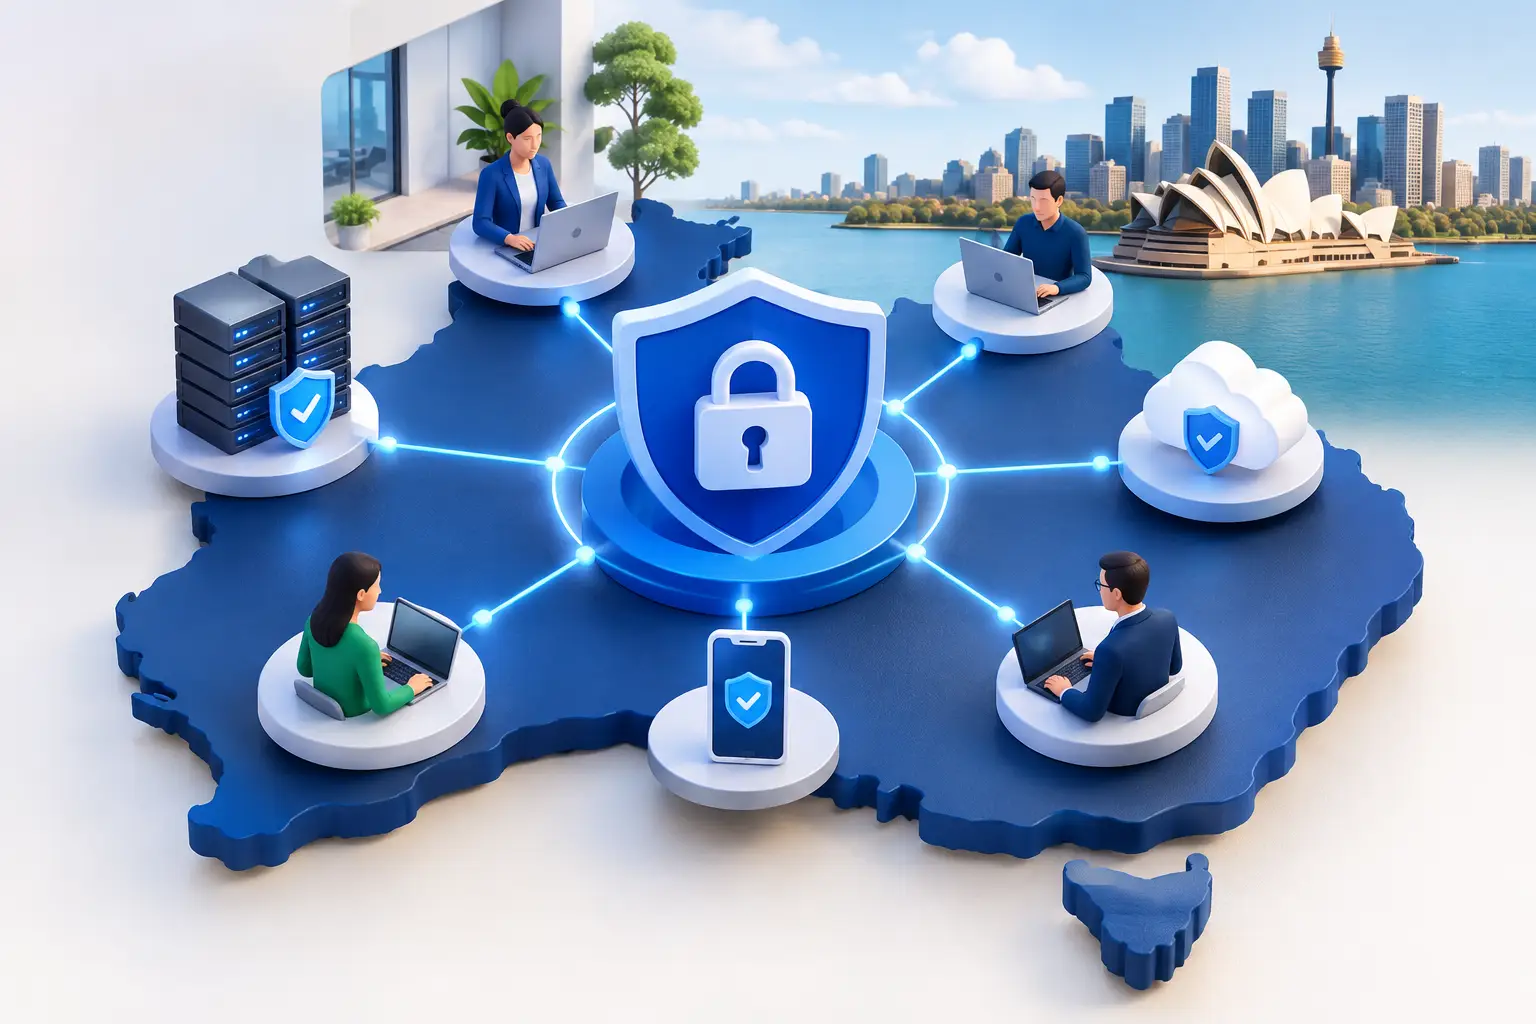
A staff member signs in from home on a managed laptop, opens a cloud app, and accesses customer records. A contractor does the same from an unfamiliar device on a mobile connection. Treating both sessions as equally trustworthy is no longer a sensible security decision. That is why zero trust trends are moving from enterprise security discussions into everyday planning for Australian businesses of every size.
Zero trust is not a single product or a switch to flick. It is an approach built on a simple principle: never assume a user, device or connection is safe simply because it is inside the network. Each request for access should be verified, given only the permissions required, and monitored for changes that could indicate risk.
For businesses managing remote staff, cloud software, branch offices and customer data, this shift is practical rather than theoretical. The aim is to reduce the damage a stolen password, compromised endpoint or malicious email can cause while keeping legitimate work moving.
Why zero trust is becoming a business priority
Traditional network security focused heavily on the office perimeter. Keep threats outside the firewall, then allow trusted users to move around inside. That model made more sense when most people worked from one location, used company-owned desktop computers and accessed systems hosted in a server room.
Those boundaries have changed. Staff may work across offices, home sites and regional locations. Core applications are often hosted in Microsoft 365, cloud platforms or specialist software-as-a-service tools. Partners, contractors and customers may need controlled access too. A business can have reliable internet and a capable firewall, yet still be exposed if an attacker signs in using a legitimate employee password.
Zero trust helps organisations make better access decisions based on context. Is the user who they claim to be? Is their device encrypted, patched and protected? Are they accessing a system they genuinely need for their role? Is the request normal for that person, location and time? The answers determine what access is granted.
Zero trust trends reshaping security decisions
Identity is becoming the primary security control
Identity and access management is at the centre of most zero trust projects. Passwords remain useful, but they cannot carry the full burden of protecting business systems. Phishing attacks, password reuse and fraudulent login pages can all turn a valid credential into an attacker’s entry point.
Multi-factor authentication is now a baseline, but the trend is moving towards phishing-resistant methods such as passkeys, security keys and number-matching authentication. These options make it harder for an attacker to capture and reuse login details. Conditional access also matters: a finance system may be available only from a compliant device, while a higher-risk sign-in triggers extra verification or is blocked.
There is a trade-off. Tighter controls can frustrate staff if they are applied without care. The better approach is to protect the highest-risk access first, then use policies that recognise normal work patterns rather than forcing every employee through the same process.
Device health matters as much as the login
A genuine user on an unsafe device can still create a serious problem. One of the most useful zero trust trends is the growing use of device posture checks before granting access to sensitive applications and data.
A device posture check can confirm whether an operating system is current, endpoint protection is active, disk encryption is enabled and the device is managed by the organisation. If a laptop is missing essential security controls, access can be limited until it is remediated.
This is particularly relevant for businesses with a mix of company devices and bring-your-own-device arrangements. A blanket ban on personal devices may not suit every organisation, especially where flexibility is needed. But personal devices should not receive the same level of access as a managed business laptop. Separate access rules, browser-based access or virtual desktop options can provide a practical middle ground.
Network access is moving closer to the application
Virtual private networks were designed to give remote users a route into a private network. They still have a role, particularly for specific legacy systems, but many organisations are moving towards application-level access through secure service edge and zero trust network access solutions.
Instead of placing a user broadly on the network, access is granted to the particular application or service they need. This reduces the opportunity for lateral movement if an account or device is compromised. It can also improve the experience for distributed teams by routing traffic through security controls designed for cloud applications, not just backhauling everything through a head office.
The right model depends on the business. A small office with a handful of cloud applications has different requirements from a multi-site organisation operating private fibre, on-premises systems and industrial devices. The common goal is to give people fast, controlled access without exposing more of the network than necessary.
Microsegmentation is reducing the blast radius
When attackers gain access, their next move is often to find more valuable systems. Microsegmentation limits that movement by separating workloads, departments and critical services into smaller security zones.
For example, a guest Wi-Fi network should not have a path to accounting systems. A compromised workstation should not be able to communicate freely with servers, backups or operational technology. Even within a cloud environment, production systems, development environments and administration tools should have deliberately defined connections.
Microsegmentation can be highly effective, but it requires planning. Businesses need to understand how applications communicate before locking down traffic. Starting with critical assets, monitoring normal connections and progressively applying policies is safer than trying to segment everything overnight.
Data protection is following the information, not the location
Data now moves between email, cloud drives, collaboration platforms, mobile devices and external partners. Zero trust increasingly focuses on protecting the data itself through classification, encryption, access controls and data loss prevention policies.
The practical question is not only, “Can this user sign in?” It is also, “Should this user be able to download, forward, print or share this information?” A payroll report, customer database export or commercial proposal deserves more protection than a public marketing document.
Not every business needs a complex classification program on day one. Begin with data that would cause the greatest financial, operational or reputational harm if exposed. Set ownership for that information, confirm where it is stored and apply proportionate controls.
Managed security is becoming a realistic option for smaller teams
Security platforms produce alerts, but alerts only help when someone can investigate and respond. For many small and mid-sized businesses, maintaining a dedicated 24/7 security operations team is not realistic. This is driving interest in managed detection and response, managed firewalls, endpoint protection and security monitoring.
A managed service should not become a black box. Business leaders still need clear visibility of what is monitored, who responds to incidents, what actions can be taken without approval and how quickly support is available. Local support is particularly valuable when an incident affects connectivity, mobiles, users and business applications at the same time.
For organisations that want connectivity and managed security under one roof, providers such as InfiNET Broadband can help align network performance, firewall management and business continuity requirements. The key is to define responsibilities clearly rather than assuming a service provider manages every risk by default.
AI is raising both the threat level and the response speed
Artificial intelligence is making phishing messages more convincing, speeding up reconnaissance and helping criminals tailor scams to businesses. It is also helping security tools identify unusual behaviour, prioritise alerts and reduce repetitive investigation work.
The sensible response is not to rely on AI as a substitute for security judgement. Security teams need well-defined policies, quality logging and people who can validate whether an alert represents a real risk. Staff awareness remains essential too. A convincing email can still bypass sophisticated controls if it persuades someone to approve a login or share sensitive information.
How to prioritise a zero trust rollout
The strongest zero trust programs are built in stages. Start with an inventory of users, devices, applications and critical data. If the business cannot identify who has access to its most important systems, it cannot properly control that access.
Next, strengthen identity. Remove inactive accounts, apply multi-factor authentication, limit administrator privileges and review access when people change roles. Then bring devices into scope by ensuring business endpoints are patched, encrypted and protected.
From there, focus on the applications and data that matter most. Apply conditional access, segment critical systems and monitor activity for unusual sign-ins, large data transfers or unexpected privilege changes. Test recovery processes as well. Zero trust reduces risk, but it does not remove the need for reliable backups and an incident response plan.
The best starting point is rarely the most complicated technology. It is a clear decision about what the business must keep available, what information it must protect and which access pathways create the greatest risk. Build controls around those priorities, review them as the business changes, and keep the experience practical for the people doing the work.