A new staff member starts on Monday, a branch relocates, or a software update needs to go live after hours. In each case, the network can either support the change quietly or turn it into a chain of manual tickets, device-by-device checks and avoidable risk. Network automation helps businesses make those routine network tasks faster, more consistent and easier to audit.
For Australian businesses with growing teams, multiple locations or a mix of cloud and on-site systems, this is about more than saving an IT team a few clicks. It is about protecting continuity of service. When internet access, cloud phone systems, payment terminals, security cameras and business applications rely on the network, small configuration errors can have a very real operational cost.
What network automation actually does
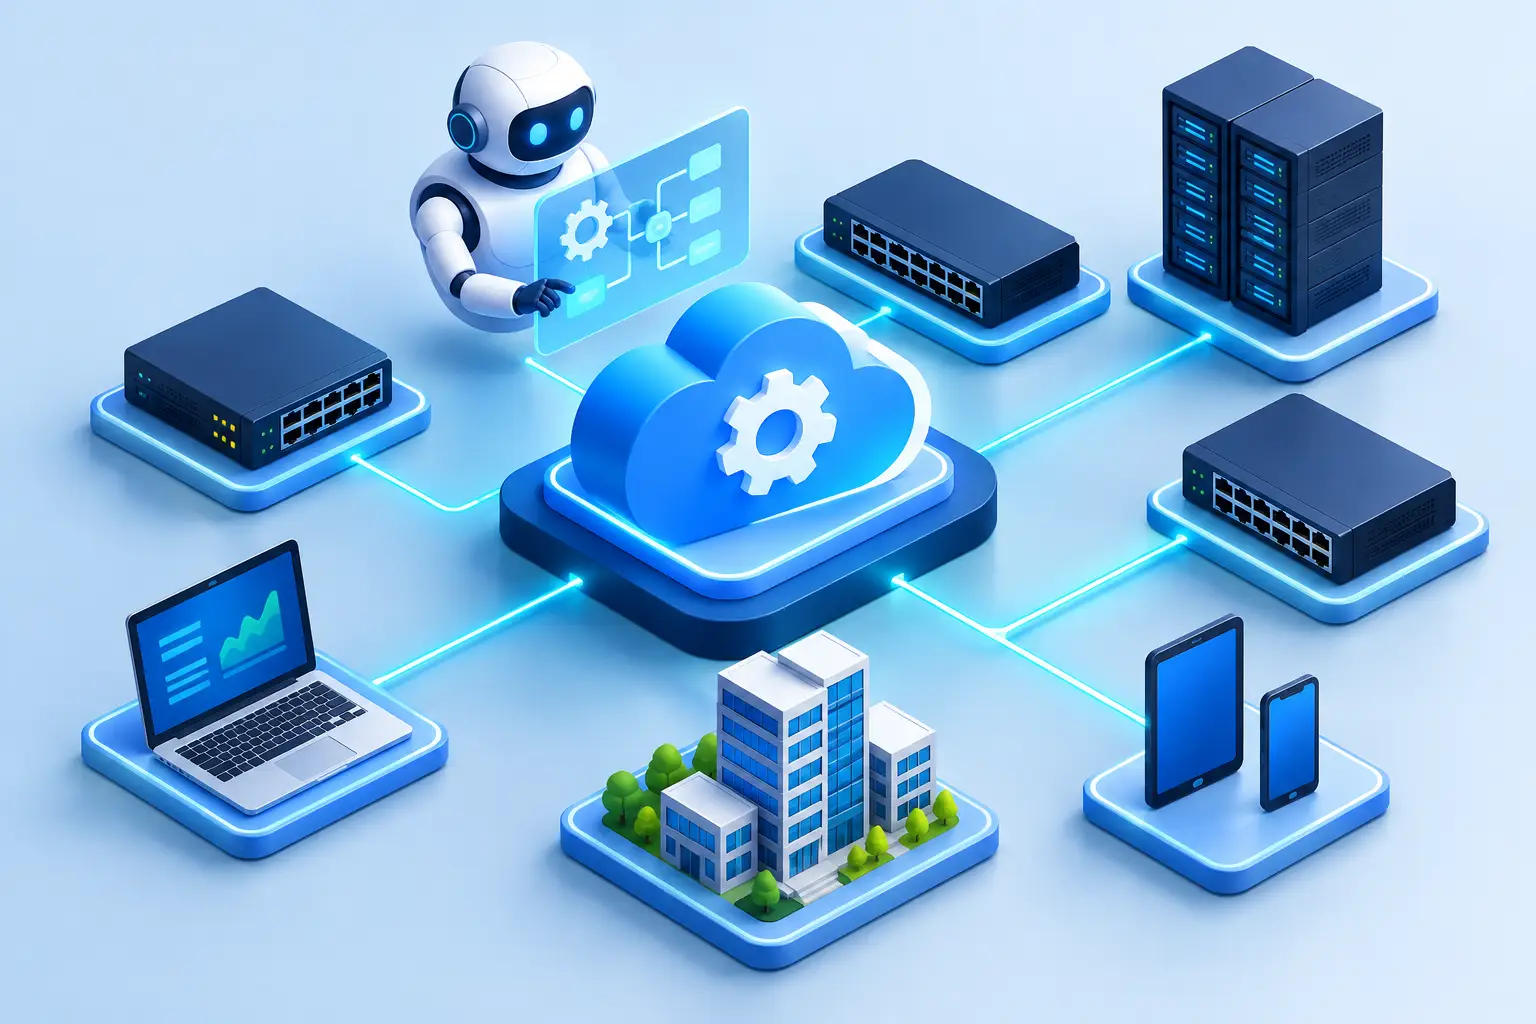
Network automation uses software, templates and rules to configure, monitor and manage network devices without relying on someone to manually repeat every task. Depending on the environment, it may cover routers, switches, Wi-Fi access points, firewalls, SD-WAN appliances and cloud networking services.
A practical example is opening a new office. Rather than configuring every device from scratch, an IT team can apply an approved configuration template for that site type. Network names, security policies, device settings and monitoring rules are deployed consistently, then adjusted only where the location has a genuine special requirement.
Automation can also respond to events. A monitoring platform might detect a failed primary connection and move approved traffic to a backup service. It might identify an unfamiliar device trying to connect, apply a defined access policy, or alert the right support contact with the diagnostic information already attached.
The goal is not to remove all human decision-making. It is to remove repetitive work where the desired outcome is known, tested and repeatable.
Where network automation delivers the strongest value
The best use cases are usually the tasks that happen often, need to be done consistently and carry a meaningful risk if handled incorrectly. For many small and mid-sized businesses, this begins with standardising how devices are configured and monitored. For enterprise organisations, it can extend across branches, private fibre, cloud environments and complex security controls.
Faster changes across multiple sites
A business with one office may be able to manage network changes manually without too much trouble. Add warehouses, retail sites, regional depots or remote staff, and that approach quickly becomes difficult to control. A single Wi-Fi or firewall policy may need to be applied in several locations, often outside business hours.
With approved templates and central management, teams can make a change once and apply it where it belongs. This reduces variation between sites and makes it easier to confirm that each location is operating to the same standard. It also helps when a device needs to be replaced, because the intended configuration is documented rather than sitting in one technician’s memory.
Better uptime and clearer fault response
Network automation cannot stop every outage. A physical fibre issue, power failure or carrier fault still needs investigation and, in some cases, a field repair. What automation can do is shorten the time between a fault occurring and the right response beginning.
For example, an automated monitoring system can identify that a primary internet connection is unavailable, test whether the issue is local or upstream, confirm whether failover has worked and notify the support team. For a business using a secondary connection such as fixed wireless, 4G/5G or satellite, predefined rules can help keep critical services operating while the primary service is restored.
That distinction matters. Automation is most valuable when it supports a continuity plan that has been designed for the business, not when it is treated as a substitute for redundancy.
Consistent security controls
Network security is often weakened by inconsistency. One branch may have an old firewall rule, another may be missing an update, and a temporary exception may remain in place long after it was needed. Those gaps are difficult to spot when changes are made manually across a large number of devices.
Automation makes it easier to apply standard access rules, schedule updates, back up configurations and check whether devices meet required security settings. It can also provide a clearer change record, which is useful when investigating an incident or meeting internal governance requirements.
However, automated security changes need care. A poorly tested rule can block legitimate systems just as efficiently as it blocks threats. Sensitive changes should have approval steps, a maintenance window where appropriate and a tested rollback plan.
Build control before you automate
The quickest way to create problems is to automate an already messy network. If naming is inconsistent, old devices are unknown, firewall rules have no owner and each location has been set up differently, automation will simply reproduce that disorder at greater speed.
Start by establishing a reliable picture of the environment. Identify the active internet services, network devices, applications that rely on fixed IP addresses, voice services, guest Wi-Fi, remote access tools and backup connections. Record who owns each system and which services are business-critical.
Next, define a standard. A branch office, for instance, may need a standard configuration for staff Wi-Fi, guest access, VoIP traffic, security cameras, network segmentation, firewall policies and monitoring. A head office or data-heavy site may need a different design. The point is not to force every location into the same mould. It is to decide what should be standard and document where exceptions are justified.
This is also the time to consider connectivity. Automation performs best when the underlying connection is fit for purpose. A site relying on cloud applications and hosted phones may need a higher-capacity NBN, OptiComm or private fibre service, while remote operations may require fixed wireless or satellite as part of a broader resilience plan.
A practical rollout for network automation
A staged rollout gives businesses a safer path than trying to automate the entire environment at once. Begin with one low-risk, high-volume task, such as configuration backups, device health checks or standard onboarding for new network equipment. Measure the result: time saved, failed changes avoided, alerts resolved sooner or improved visibility.
Once the process is proven, move to more operationally important workflows. This may include automating approved firewall updates, provisioning new sites, managing SD-WAN policies or switching selected services to a backup connection during an outage.
Good automation should be predictable. Every workflow needs a clear trigger, defined permissions, an audit trail and a way to stop or reverse the action if something does not look right. Test changes in a controlled environment where possible, particularly when they affect phones, point-of-sale systems, remote access or production applications.
It is also worth setting realistic expectations. Automation can reduce configuration time from hours to minutes, but it will not make poor internet capacity disappear or resolve an unclear business policy. It works alongside sound network design, suitable bandwidth, quality hardware and responsive support.
Automation still needs people
The businesses that get the most from automation do not treat it as a set-and-forget tool. They assign ownership, review alerts and regularly assess whether the automated rules still match how the organisation operates.
A growing business may only need a straightforward setup with managed Wi-Fi, a business-grade firewall and central monitoring. A multi-site organisation may need SD-WAN, segmented networks, failover services and more detailed security controls. The right approach depends on the number of locations, the cost of downtime, compliance needs and the skills available internally.
For teams without a dedicated network specialist, a managed provider can help design the standards, monitor the environment and provide local support when an issue needs human judgement. InfiNET Broadband can pair business connectivity with managed networking and security services, helping organisations avoid the disconnect between the internet service and the systems that depend on it.
Make reliability repeatable
Network automation is most useful when it makes ordinary work more dependable: a new site opens with the right settings, a replacement device is configured correctly, a fault is detected early and a security policy is applied consistently. Start with the repeatable task causing the most friction, make it safe and measurable, then build from there. That is how automation becomes a practical part of business continuity rather than another layer of technology to manage.