A suspicious email is opened by an employee. A file runs quietly in the background, steals a browser session or begins encrypting shared files. The question is not simply whether your antivirus recognises it. The real question is: how does EDR stop threats once activity on a laptop, server or mobile device starts to look wrong?
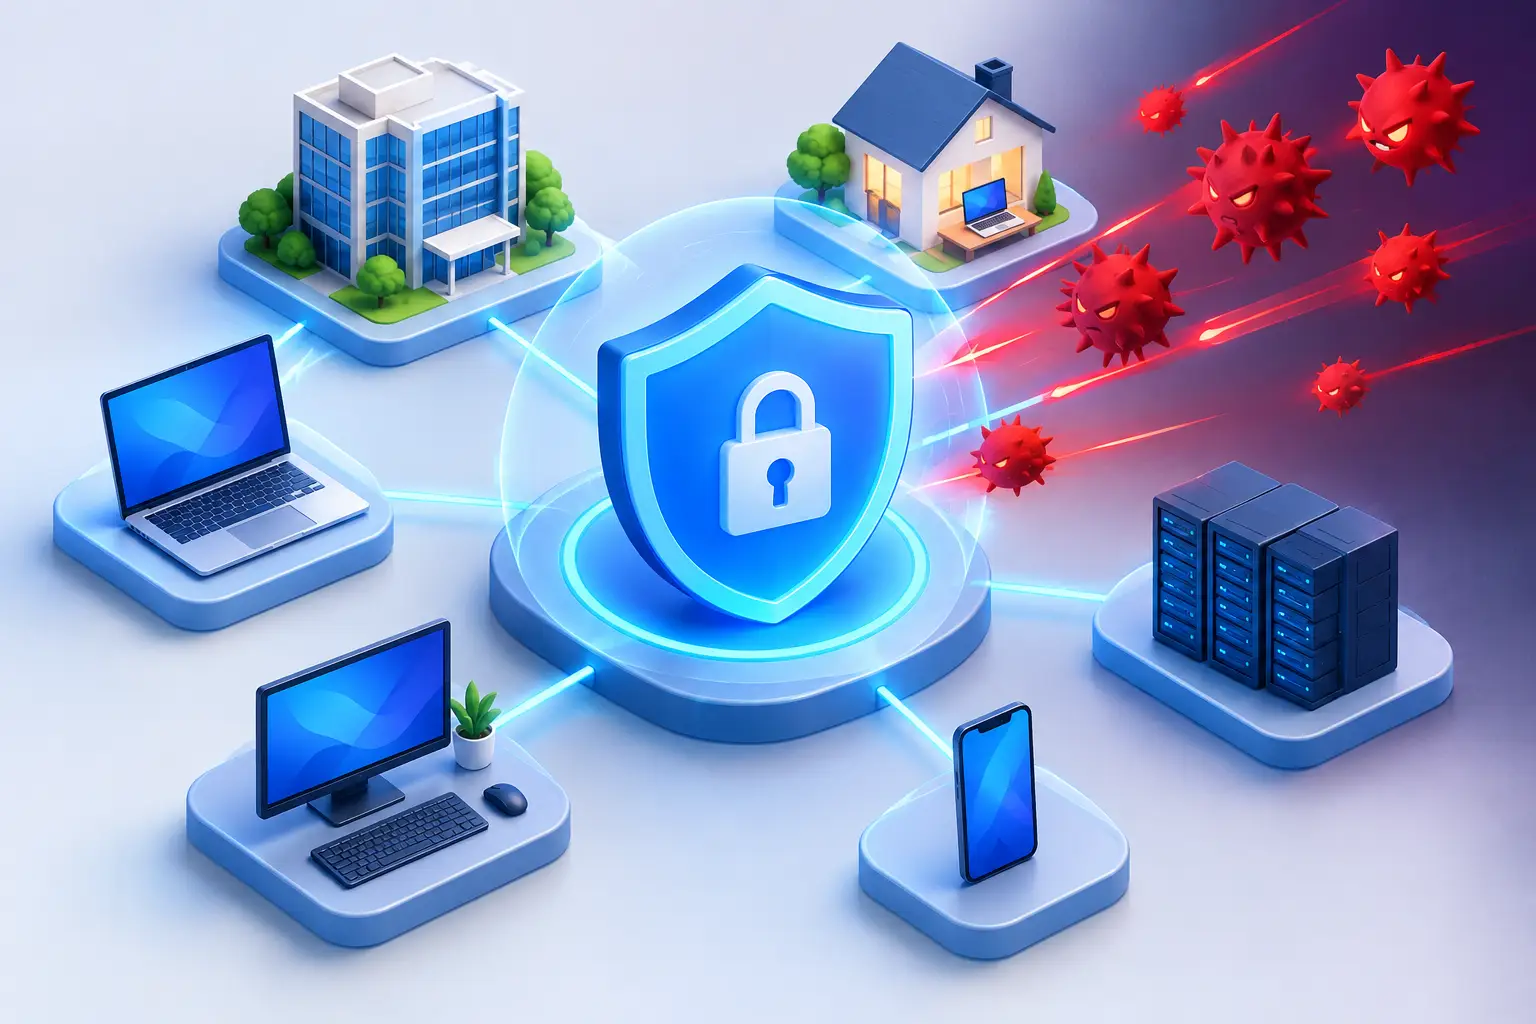
Endpoint Detection and Response, or EDR, gives businesses visibility and control at the point where people work: their endpoints. That includes office PCs, work-from-home laptops, servers and, depending on the platform, mobile devices. Rather than relying only on known malware signatures, EDR watches for behaviour that may signal an attack, then helps security teams investigate and contain it.
For Australian businesses that depend on cloud apps, business phones, shared data and reliable connectivity, that speed matters. A security event can quickly become a service interruption, a privacy issue or a costly recovery exercise.
What EDR actually does
EDR is endpoint security designed to continuously collect and analyse activity from devices across your organisation. It records useful security telemetry such as processes that run, files that change, network connections, user activity and attempts to alter security settings.
This creates a timeline of what happened on a device. If an attacker gains access through a malicious attachment, a compromised password or an unpatched application, EDR can show the chain of activity rather than presenting a single isolated alert.
Traditional antivirus remains useful. It can block many known malicious files before they run. EDR goes further by looking for suspicious actions, including behaviours that may not match a known threat. It is particularly valuable when attackers use legitimate tools already present in an operating system, or when a new form of malware has not yet been identified by a signature.
How does EDR stop threats in practice?
EDR does not make risk disappear, and it cannot replace sound access controls, patching or staff awareness. What it does is shorten the time between an attack beginning and your team being able to stop its spread. That process generally involves detection, investigation, containment and recovery.
It detects suspicious behaviour, not just bad files
Modern attacks do not always arrive as obvious malware. An attacker may use a stolen Microsoft 365 login, command-line tools, remote access software or a trusted application to move through a network. A basic file scan can miss this activity because the individual tool may be legitimate.
EDR looks at context. For example, it may flag a document application launching a command shell, a workstation attempting to access dozens of shared folders in minutes, or a new process disabling security services. It can also identify unusual outbound connections, repeated failed logins or a sudden burst of file encryption.
A single event may be harmless. A technician running an approved script, for instance, can trigger behaviour that looks unusual. EDR is most effective when it correlates several signals and applies policies that reflect how your business operates.
It blocks or isolates the affected endpoint
When a threat reaches a defined level of risk, EDR can take automated action. Depending on the product and policy, it may terminate a malicious process, quarantine a file, block a connection or prevent the program from running again.
One of the most useful response actions is device isolation. The endpoint can remain connected to the security platform while being cut off from the wider network. This helps stop ransomware reaching file servers, prevents lateral movement to other computers and gives an IT team time to investigate without pulling the plug on every system.
Isolation is powerful, but it needs sensible configuration. Automatically isolating every device that generates a medium-risk alert could interrupt a busy accounting team, warehouse operation or remote workforce. Many organisations use automation for high-confidence threats and require human review for less certain events.
It reveals the attack path
Containment is only the first step. A business also needs to know how the event started, what it touched and whether the attacker still has another way in.
EDR investigation tools can trace activity back through a process tree. They may show that a user downloaded a file, the file launched a script, the script created a scheduled task and that task attempted to contact an external server. This evidence helps IT teams remove persistence mechanisms and identify other endpoints with the same indicators.
That visibility is especially helpful after a phishing incident or suspected credential compromise. Instead of manually checking each device, security staff can search their endpoint fleet for the same file hash, command, domain or behaviour. Faster scoping means fewer assumptions and a more targeted response.
It supports recovery without losing the evidence
After an incident, it is tempting to rebuild the affected computer and move on. Sometimes that is the right operational choice. However, removing a device too quickly can erase clues that explain how the attacker entered and whether other systems remain exposed.
EDR retains event data that can support a structured recovery. Your team can confirm the malicious file was removed, reset credentials where necessary, patch the underlying weakness and monitor for repeat activity. The result is not just a cleaned endpoint, but a clearer understanding of what needs to change.
Why endpoint visibility matters for hybrid businesses
The old network perimeter is no longer the only place to protect. Employees work from home, use cloud applications, connect through VPNs and access business systems from regional locations. A laptop can be exposed on a home Wi-Fi connection one day and connected to the office network the next.
EDR follows the endpoint, wherever it is operating. That makes it a practical layer of protection for organisations with a mixture of office staff, field teams and remote workers. It can also provide consistent security oversight when different sites use different internet services or network layouts.
For a small business, this may mean knowing whether a compromised laptop is trying to access cloud files. For a multi-site organisation, it can mean containing one affected device before it disrupts operations at other locations. The business benefit is continuity: fewer incidents that become all-hands emergencies.
EDR works best as part of a wider security approach
EDR is not a substitute for a managed firewall, secure email controls, multifactor authentication, backups or regular updates. Each layer addresses a different part of the attack path.
Multifactor authentication can reduce the chance that a stolen password gives an attacker access. Email filtering can block many phishing messages before staff see them. Firewalls can control network traffic, while tested backups give you a recovery option if an incident succeeds. EDR provides the endpoint-level detection and response that ties into this broader picture.
The right setup depends on your business. A small professional services firm may need managed endpoint protection with clear escalation support. A larger organisation may require centralised monitoring, policy management across hundreds of devices and integration with its existing security operations. In either case, clear ownership matters. Someone needs to review alerts, tune policies and act when a device is isolated.
Questions to ask before choosing EDR
Start with the endpoints you need to protect. Include company laptops, desktops, servers and devices used by remote employees. Check whether the EDR service supports the operating systems you use and whether server coverage is licensed separately.
Then consider who will monitor it. An EDR platform can generate valuable alerts, but alerts left unread do not protect a business. If you do not have an internal IT security team, a managed service can provide monitoring, response guidance and a clear path for escalation.
Also ask how the product affects performance, privacy and day-to-day support. Endpoint agents use system resources, although well-designed tools are usually light enough for normal business use. Your policies should balance strong protection with the practical need for staff to keep working. Finally, confirm how incident data is retained and how quickly you can access support when an alert needs urgent attention.
InfiNET Broadband can help businesses bring connectivity, managed security and endpoint protection into a more practical service model, with local Aussie support when continuity matters.
The best time to test your response is before a real incident. Review which devices are covered, confirm who receives alerts after hours and make sure your team knows the steps to take when EDR isolates a machine. A fast, calm response can be the difference between one compromised endpoint and a business-wide outage.