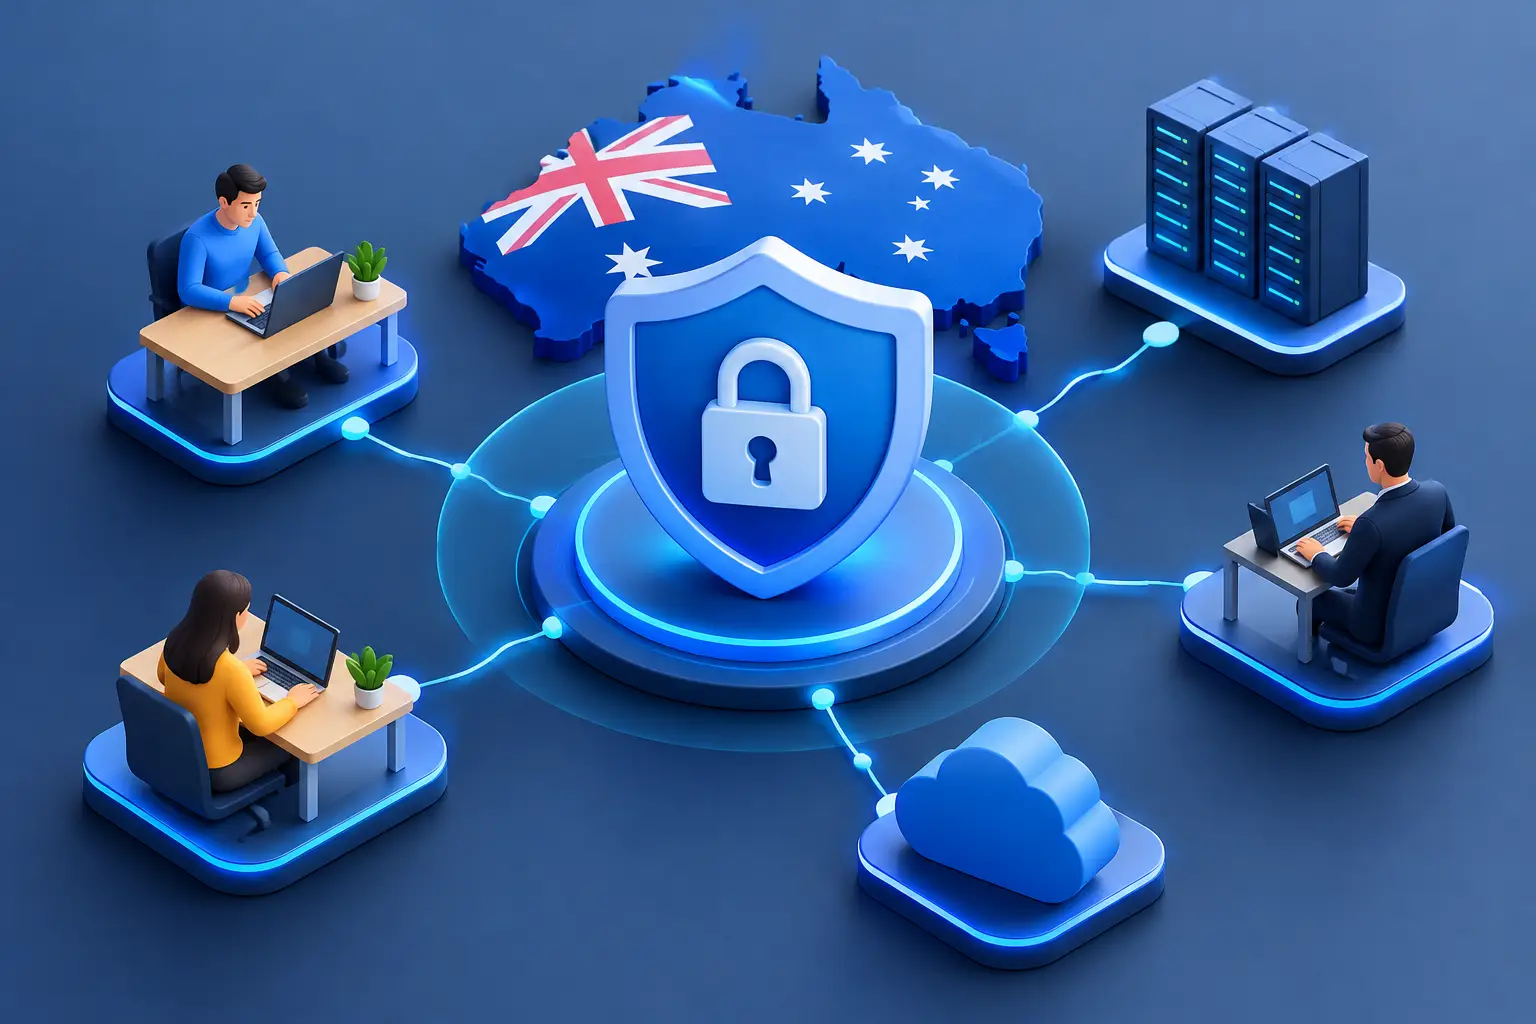
A single compromised password can give an attacker far more access than it should. For businesses using cloud software, remote staff, mobile devices and multiple sites, zero trust is a practical way to limit that exposure without making daily work harder than necessary.
The approach is simple: never grant access just because a person or device is connected to the business network. Instead, verify who is requesting access, check the context of that request, and allow only the access needed for the task at hand. It is a better fit for the way many Australian businesses now operate – across offices, home workspaces, warehouses, regional sites and cloud platforms.
What zero trust means in practice
Traditional network security often worked on a perimeter model. If someone was inside the office network, connected through a VPN or using an approved device, they could be treated as trusted. That made sense when applications, files and staff were largely in one building.
That boundary has changed. Teams now access Microsoft 365, cloud accounting platforms, customer records, phone systems and internal applications from many locations. A user may be legitimate, but their password could be stolen, their laptop could be infected, or their session could be hijacked. Once an attacker gets through a weak point, broad network access can turn a small incident into a serious outage.
Zero trust replaces blanket trust with continuous checks. A staff member logging into email from their usual managed laptop in Sydney may be allowed through with minimal interruption. The same account attempting to download sensitive files from an unfamiliar device overseas may be asked for further verification or blocked outright.
This does not mean assuming employees are doing the wrong thing. It means designing security around the reality that credentials, devices and networks can all be compromised.
Why zero trust matters for connected businesses
For a small business, a cyber incident can stop invoicing, customer service, payroll and communications at the same time. For a multi-site organisation, the impact can spread across branches, field teams and shared systems. Downtime is not only an IT problem – it can mean missed sales, delayed projects and frustrated customers.
Zero trust helps reduce the chance that one stolen credential becomes unrestricted access. It also improves visibility. Rather than relying on a broad statement that a user is “on the network”, IT teams can see who accessed which application, from what device, where they were located and whether that access was appropriate.
This is particularly useful for businesses with a mix of office staff, remote workers, contractors and managed service providers. Access can be set around roles and responsibilities. A bookkeeper may need finance software but not network administration tools. A contractor may need access to one project folder for a defined period, not a permanent pathway into every business system.
There is a trade-off. More checks can create friction if they are poorly planned. The answer is not to apply the strictest possible rule to every person and every system. The answer is to apply controls proportionately, with stronger protection around high-risk accounts, critical data and sensitive business operations.
The building blocks of a zero trust approach
Zero trust is not one product that can be switched on overnight. It is a security strategy built from several controls that work together. Most businesses can make meaningful progress by improving the fundamentals first.
Confirm identity with multi-factor authentication
Multi-factor authentication, or MFA, should be a baseline for email, cloud applications, remote access and administrative accounts. A password alone is no longer enough protection, especially where passwords are reused, guessed or captured through phishing.
MFA adds another check, such as an authenticator app, security key or approval prompt. For higher-risk users – including administrators, finance staff and executives – phishing-resistant methods such as security keys may be worth considering. SMS codes can be better than no MFA, but they are generally less resilient than app-based or hardware options.
Check the device, not only the user
A genuine employee using an unmanaged or out-of-date device can still create risk. Device policies can check whether a computer has current operating system updates, disk encryption, endpoint protection and screen-lock settings before allowing access to business services.
For a business with company-issued laptops, this is usually easier to enforce. Bring-your-own-device arrangements need more care. You may choose to allow personal mobiles to access email but prevent them from downloading sensitive files, or require data to stay within managed applications. The right balance depends on the work being done and the information involved.
Limit access to what each person needs
Least-privilege access is a core zero trust principle. Give people the permissions required for their role, and no more. This includes staff accounts, shared mailboxes, cloud storage, business applications and administrator privileges.
Review access when someone changes roles, finishes a contract or leaves the business. These events are often overlooked, particularly in growing organisations where systems have been added over time. Removing unnecessary permissions is one of the most direct ways to reduce exposure.
Administrator accounts deserve special attention. Daily work should be completed using a standard account where possible, with elevated access used only for specific tasks. This helps contain the damage if a routine account is compromised.
Segment networks and protect critical services
Not every device should be able to communicate freely with every other device. Network segmentation separates systems so that an incident in one area is less likely to spread.
For example, guest Wi-Fi should be separate from internal business systems. Internet-connected cameras, printers and smart devices should not sit unrestricted alongside finance workstations or servers. A retail site, warehouse or development location may also need separate rules based on operational requirements.
Firewalls, secure remote access, managed Wi-Fi and SD-WAN can all support segmentation across one or many sites. The design matters more than a checklist of products. A small office will have different needs from an enterprise operating private fibre, cloud workloads and multiple branches.
Monitor activity and respond early
Verification is not a one-time event at sign-in. Security logs and alerts can identify unusual behaviour, such as impossible travel, repeated failed login attempts, a sudden request for elevated privileges or an unexpected volume of data downloads.
Monitoring only helps when someone is responsible for acting on it. Establish clear steps for investigating suspicious activity, disabling accounts, isolating devices and communicating with affected staff or customers. For businesses without an internal security team, a managed security provider can provide useful coverage and escalation support.
How to introduce zero trust without disrupting operations
Start by identifying the systems that would cause the greatest disruption if they were unavailable or compromised. For many businesses, that includes email, cloud storage, finance platforms, customer databases, phone systems, remote access and administrator accounts.
Then map who needs access and how they connect. This often reveals old accounts, overly broad shared folders, unsupported devices and services that have no MFA enabled. Fixing these obvious gaps can deliver an immediate improvement before a larger security project begins.
A sensible rollout commonly starts with MFA for all users, followed by stronger protections for privileged accounts and sensitive applications. Next, introduce device management, conditional access rules and network segmentation in stages. Test policies with a small group before applying them company-wide, particularly where staff need reliable access from regional locations or while travelling.
Clear communication is essential. Staff are more likely to follow security controls when they understand why a new prompt, device policy or access restriction exists. Keep instructions simple, provide a support contact and plan for exceptions that are genuinely required for business continuity.
InfiNET Broadband can support businesses that need dependable connectivity alongside managed security, firewall and network solutions. Security controls work best when the underlying internet, Wi-Fi and remote access design is reliable enough for staff to use confidently.
Zero trust is a business continuity decision
Zero trust will not prevent every cyber incident. A determined attacker, an unpatched system or a convincing scam can still create risk. What it does is reduce unnecessary access, make suspicious activity easier to spot and limit how far an incident can travel.
The best starting point is not a complicated security transformation. It is a clear question: if one account or device were compromised tomorrow, what could it reach? Each practical control that narrows that answer gives your business a stronger chance of keeping services running when it matters most.